Vulnerability Scan Result

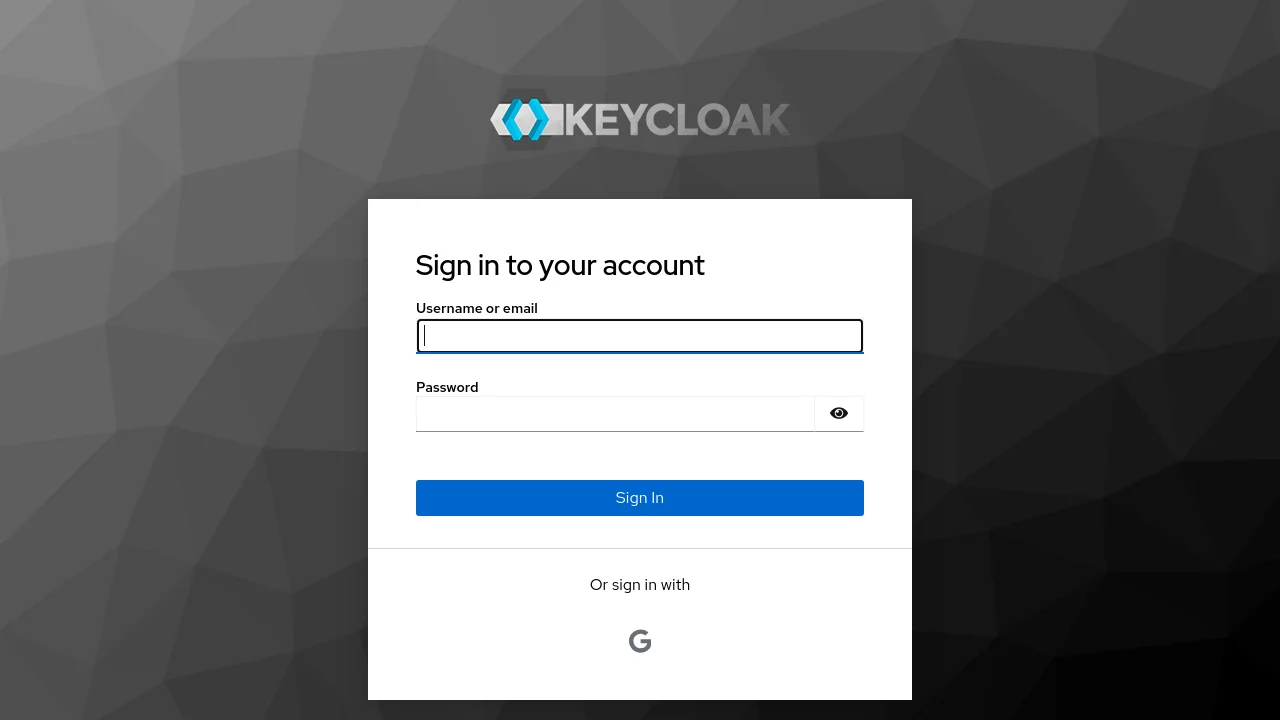
| Title: | No title found |
| Description: | No description found |
| ip_address | 34.123.10.204 |
| country | US  |
| network_name | Google LLC |
| asn | AS396982 |
80/tcp | http | kong/3.9.1 - |
443/tcp | https | kong/3.9.1 - |
No technologies could be detected.
Web Application Vulnerabilities
Evidence
| URL | Evidence |
|---|---|
| https://goldilocks.demand-services.io/ | HTTP authentication found in header |
Vulnerability description
We have discovered that the target application presents a login interface that could be a potential target for attacks. While login interfaces are standard for user authentication, they can become vulnerabilities if not properly secured.
Risk description
The risk is that an attacker could use this interface to mount brute force attacks against known passwords and usernames combinations leaked throughout the web.
Recommendation
Ensure each interface is not bypassable using common knowledge of the application or leaked credentials using occasional password audits.
Classification
| CWE | CWE-287 |
| OWASP Top 10 - 2017 | |
| OWASP Top 10 - 2021 |
Vulnerability description
We have noticed that the server is missing the security.txt file, which is considered a good practice for web security. It provides a standardized way for security researchers and the public to report security vulnerabilities or concerns by outlining the preferred method of contact and reporting procedures.
Risk description
There is no particular risk in not having a security.txt file for your server. However, this file is important because it offers a designated channel for reporting vulnerabilities and security issues.
Recommendation
We recommend you to implement the security.txt file according to the standard, in order to allow researchers or users report any security issues they find, improving the defensive mechanisms of your server.
Classification
| CWE | CWE-1188 |
| OWASP Top 10 - 2017 | |
| OWASP Top 10 - 2021 |
Infrastructure Vulnerabilities
Evidence
| Operating System | Accuracy |
|---|---|
| Crestron XPanel control system | 90% |
Vulnerability description
OS Detection
Evidence
| Domain Queried | DNS Record Type | Description | Value |
|---|---|---|---|
| goldilocks.demand-services.io | A | IPv4 address | 34.123.10.204 |
Risk description
An initial step for an attacker aiming to learn about an organization involves conducting searches on its domain names to uncover DNS records associated with the organization. This strategy aims to amass comprehensive insights into the target domain, enabling the attacker to outline the organization's external digital landscape. This gathered intelligence may subsequently serve as a foundation for launching attacks, including those based on social engineering techniques. DNS records pointing to services or servers that are no longer in use can provide an attacker with an easy entry point into the network.
Recommendation
We recommend reviewing all DNS records associated with the domain and identifying and removing unused or obsolete records.