Vulnerability Scan Result

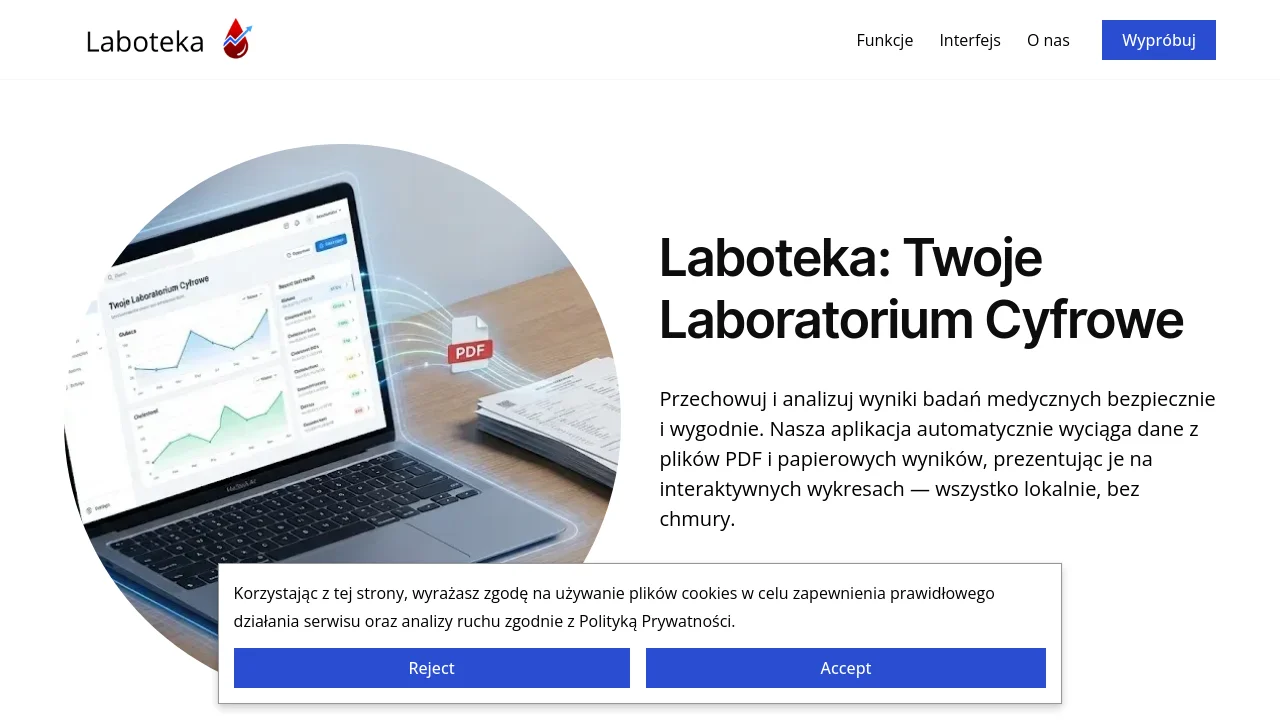
| Title: | |
| Description: |
| ip_address | 34.128.166.114 |
| country | US  |
| network_name | Google LLC |
| asn | AS396982 |
80/tcp | http | - - |
443/tcp | https | - - |
| Software / Version | Category |
|---|---|
| Reddit Ads | Advertising |
| Microsoft Clarity | Analytics |
| Google Cloud | IaaS |
| Google Cloud CDN | CDN |
| Google Cloud Load Balancing | Load balancers |
| Google Cloud Trace | Performance |
| Google Sign-in | Authentication |
| Facebook Pixel 2.9.408 | Analytics |
| Bootstrap 5.2.3 | UI frameworks |
| core-js 3.32.2 | JavaScript libraries |
| Google Analytics GA4 | Analytics |
| HTTP/3 | Miscellaneous |
| MySQL | Databases |
| Next.js 15.5.21 | JavaScript frameworks, Web frameworks, Web servers, Static site generator |
| HeroUI | UI frameworks |
| Open Graph | Miscellaneous |
| PHP | Programming languages |
| PostHog | Analytics |
| React | JavaScript frameworks |
| React Router 6 | JavaScript frameworks |
| Sentry | Issue trackers |
| Solo | Page builders |
| DoubleClick Floodlight | Advertising |
| PWA | Miscellaneous |
| Webpack | Miscellaneous |
| Priority Hints | Performance |
| WordPress | CMS, Blogs |
| reCAPTCHA | Security |
| Google Tag Manager | Tag managers |
| Netlify | PaaS, CDN |
| HSTS | Security |
| Strava | Widgets |
| Varnish | Caching |
Web Application Vulnerabilities
Evidence
| CVE | CVSS | EPSS Score | EPSS Percentile | Summary |
|---|---|---|---|---|
| CVE-2026-27980 | 6.9 | 0.00841 | 0.56044 | Next.js is a React framework for building full-stack web applications. Starting in version 10.0.0 and prior to version 16.1.7, the default Next.js image optimization disk cache (`/_next/image`) did not have a configurable upper bound, allowing unbounded cache growth. An attacker could generate many unique image-optimization variants and exhaust disk space, causing denial of service. This is fixed in version 16.1.7 by adding an LRU-backed disk cache with `images.maximumDiskCacheSize`, including eviction of least-recently-used entries when the limit is exceeded. Setting `maximumDiskCacheSize: 0` disables disk caching. If upgrading is not immediately possible, periodically clean `.next/cache/images` and/or reduce variant cardinality (e.g., tighten values for `images.localPatterns`, `images.remotePatterns`, and `images.qualities`). |
| CVE-2025-59472 | 5.9 | 0.00417 | 0.33244 | A denial of service vulnerability exists in Next.js versions with Partial Prerendering (PPR) enabled when running in minimal mode. The PPR resume endpoint accepts unauthenticated POST requests with the `Next-Resume: 1` header and processes attacker-controlled postponed state data. Two closely related vulnerabilities allow an attacker to crash the server process through memory exhaustion: 1. **Unbounded request body buffering**: The server buffers the entire POST request body into memory using `Buffer.concat()` without enforcing any size limit, allowing arbitrarily large payloads to exhaust available memory. 2. **Unbounded decompression (zipbomb)**: The resume data cache is decompressed using `inflateSync()` without limiting the decompressed output size. A small compressed payload can expand to hundreds of megabytes or gigabytes, causing memory exhaustion. Both attack vectors result in a fatal V8 out-of-memory error (`FATAL ERROR: Reached heap limit Allocation failed - JavaScript heap out of memory`) causing the Node.js process to terminate. The zipbomb variant is particularly dangerous as it can bypass reverse proxy request size limits while still causing large memory allocation on the server. To be affected you must have an application running with `experimental.ppr: true` or `cacheComponents: true` configured along with the NEXT_PRIVATE_MINIMAL_MODE=1 environment variable. Strongly consider upgrading to 15.6.0-canary.61 or 16.1.5 to reduce risk and prevent availability issues in Next applications. |
Vulnerability description
Outdated or vulnerable software components include versions of server-side software that are no longer supported or have known, publicly disclosed vulnerabilities. Using outdated software significantly increases the attack surface of a system and may allow unauthorized access, data leaks, or service disruptions. Vulnerabilities in these components are often well-documented and actively exploited by attackers. Without security patches or vendor support, any weaknesses remain unmitigated, exposing the application to risks. In some cases, even after patching, the reported version may remain unchanged, requiring manual verification.
Risk description
The risk is that an attacker could search for an appropriate exploit (or create one himself) for any of these vulnerabilities and use it to attack the system. Since the vulnerabilities were discovered using only version-based testing, the risk level for this finding will not exceed 'high' severity. Critical risks will be assigned to vulnerabilities identified through accurate active testing methods.
Recommendation
In order to eliminate the risk of these vulnerabilities, we recommend you check the installed software version and upgrade to the latest version.
Classification
| CWE | CWE-1035 |
| OWASP Top 10 - 2017 | |
| OWASP Top 10 - 2021 |
Evidence
| Software / Version | Category |
|---|---|
| Reddit Ads | Advertising |
| Microsoft Clarity | Analytics |
| Google Cloud | IaaS |
| Google Cloud CDN | CDN |
| Google Cloud Load Balancing | Load balancers |
| Google Cloud Trace | Performance |
| Google Sign-in | Authentication |
| Facebook Pixel 2.9.408 | Analytics |
| Bootstrap 5.2.3 | UI frameworks |
| core-js 3.32.2 | JavaScript libraries |
| Google Analytics GA4 | Analytics |
| HTTP/3 | Miscellaneous |
| MySQL | Databases |
| Next.js 15.5.21 | JavaScript frameworks, Web frameworks, Web servers, Static site generator |
| HeroUI | UI frameworks |
| Open Graph | Miscellaneous |
| PHP | Programming languages |
| PostHog | Analytics |
| React | JavaScript frameworks |
| React Router 6 | JavaScript frameworks |
| Sentry | Issue trackers |
| Solo | Page builders |
| DoubleClick Floodlight | Advertising |
| PWA | Miscellaneous |
| Webpack | Miscellaneous |
| Priority Hints | Performance |
| WordPress | CMS, Blogs |
| reCAPTCHA | Security |
| Google Tag Manager | Tag managers |
| Netlify | PaaS, CDN |
| HSTS | Security |
| Strava | Widgets |
| Varnish | Caching |
Vulnerability description
We noticed that server software and technology details are exposed, potentially aiding attackers in tailoring specific exploits against identified systems and versions.
Risk description
The risk is that an attacker could use this information to mount specific attacks against the identified software type and version.
Recommendation
We recommend you to eliminate the information which permits the identification of software platform, technology, server and operating system: HTTP server headers, HTML meta information, etc.
Classification
| CWE | CWE-200 |
| OWASP Top 10 - 2017 | |
| OWASP Top 10 - 2021 |
Vulnerability description
We have noticed that the server is missing the security.txt file, which is considered a good practice for web security. It provides a standardized way for security researchers and the public to report security vulnerabilities or concerns by outlining the preferred method of contact and reporting procedures.
Risk description
There is no particular risk in not having a security.txt file for your server. However, this file is important because it offers a designated channel for reporting vulnerabilities and security issues.
Recommendation
We recommend you to implement the security.txt file according to the standard, in order to allow researchers or users report any security issues they find, improving the defensive mechanisms of your server.
Classification
| CWE | CWE-1188 |
| OWASP Top 10 - 2017 | |
| OWASP Top 10 - 2021 |
Infrastructure Vulnerabilities
Evidence
| CVE | CVSS | EPSS Score | EPSS Percentile | CISA KEV | Summary |
|---|---|---|---|---|---|
| CVE-2026-27980 | 6.9 | 0.00841 | 0.56044 | No | Next.js is a React framework for building full-stack web applications. Starting in version 10.0.0 and prior to version 16.1.7, the default Next.js image optimization disk cache (`/_next/image`) did not have a configurable upper bound, allowing unbounded cache growth. An attacker could generate many unique image-optimization variants and exhaust disk space, causing denial of service. This is fixed in version 16.1.7 by adding an LRU-backed disk cache with `images.maximumDiskCacheSize`, including eviction of least-recently-used entries when the limit is exceeded. Setting `maximumDiskCacheSize: 0` disables disk caching. If upgrading is not immediately possible, periodically clean `.next/cache/images` and/or reduce variant cardinality (e.g., tighten values for `images.localPatterns`, `images.remotePatterns`, and `images.qualities`). |
| CVE-2025-59472 | 5.9 | 0.00417 | 0.33244 | No | A denial of service vulnerability exists in Next.js versions with Partial Prerendering (PPR) enabled when running in minimal mode. The PPR resume endpoint accepts unauthenticated POST requests with the `Next-Resume: 1` header and processes attacker-controlled postponed state data. Two closely related vulnerabilities allow an attacker to crash the server process through memory exhaustion: 1. **Unbounded request body buffering**: The server buffers the entire POST request body into memory using `Buffer.concat()` without enforcing any size limit, allowing arbitrarily large payloads to exhaust available memory. 2. **Unbounded decompression (zipbomb)**: The resume data cache is decompressed using `inflateSync()` without limiting the decompressed output size. A small compressed payload can expand to hundreds of megabytes or gigabytes, causing memory exhaustion. Both attack vectors result in a fatal V8 out-of-memory error (`FATAL ERROR: Reached heap limit Allocation failed - JavaScript heap out of memory`) causing the Node.js process to terminate. The zipbomb variant is particularly dangerous as it can bypass reverse proxy request size limits while still causing large memory allocation on the server. To be affected you must have an application running with `experimental.ppr: true` or `cacheComponents: true` configured along with the NEXT_PRIVATE_MINIMAL_MODE=1 environment variable. Strongly consider upgrading to 15.6.0-canary.61 or 16.1.5 to reduce risk and prevent availability issues in Next applications. |
Vulnerability description
Vulnerabilities found for Next.js 15.5.21
Risk description
These vulnerabilities expose the affected applications to the risk of unauthorized access to confidential data and possibly to denial of service attacks. An attacker could search for an appropriate exploit (or create one) for any of these vulnerabilities and use it to attack the system. Notes: - The vulnerabilities are identified based on the server's version.; - Only the first 5 vulnerabilities with the highest risk are shown for each port.; Since the vulnerabilities were discovered using only version-based testing, the risk level for this finding will not exceed "high" severity. Critical risks will be assigned to vulnerabilities identified through accurate active testing methods.
Recommendation
We recommend you to upgrade the affected software to the latest version in order to eliminate the risks imposed by these vulnerabilities.
Evidence
We found insecure DNS cookie usage on the following nameservers: arely.ns.cloudflare.com, ray.ns.cloudflare.com
Vulnerability description
We found that the server does not implement DNS Cookies or uses them insecurely. DNS Cookies help prevent DNS-based attacks, such as spoofing and amplification attacks.
Risk description
The risk exists because without DNS Cookies, the server is vulnerable to DNS spoofing and amplification attacks. Attackers can manipulate responses or use the server in distributed denial-of-service (DDoS) attacks, compromising network availability and security.
Recommendation
We recommend enabling DNS Cookies to prevent spoofed DNS responses. Ensure proper cookie validation is implemented to mitigate DNS amplification attacks. Regularly update DNS servers to support the latest DNS security features.
Evidence
| Software / Version | Category |
|---|---|
| WordPress | CMS, Blogs |
| Next.js 15.5.21 | JavaScript frameworks, Web frameworks, Web servers, Static site generator |
| Solo | Page builders |
| Sentry | Issue trackers |
| MySQL | Databases |
| PHP | Programming languages |
| Google Sign-in | Authentication |
| HeroUI | UI frameworks |
| Bootstrap 5.2.3 | UI frameworks |
| Varnish | Caching |
| Google Cloud Load Balancing | Load balancers |
| React | JavaScript frameworks |
| Google Cloud | IaaS |
| React Router 6 | JavaScript frameworks |
| Priority Hints | Performance |
| Reddit Ads | Advertising |
| PostHog | Analytics |
| Microsoft Clarity | Analytics |
| Google Tag Manager | Tag managers |
| Google Analytics GA4 | Analytics |
| Facebook Pixel 2.9.408 | Analytics |
| core-js 3.32.2 | JavaScript libraries |
| DoubleClick Floodlight | Advertising |
| Strava | Widgets |
| reCAPTCHA | Security |
| Netlify | PaaS, CDN |
| HSTS | Security |
| Google Cloud Trace | Performance |
| Webpack | Miscellaneous |
| Open Graph | Miscellaneous |
| PWA | Miscellaneous |
| HTTP/3 | Miscellaneous |
| Google Cloud CDN | CDN |
Vulnerability description
We noticed that server software and technology details are exposed, potentially aiding attackers in tailoring specific exploits against identified systems and versions.
Risk description
The risk is that an attacker could use this information to mount specific attacks against the identified software type and version.
Recommendation
We recommend you to eliminate the information which permits the identification of software platform, technology, server and operating system: HTTP server headers, HTML meta information, etc.
Evidence
| Operating System | Accuracy |
|---|---|
| FreeBSD 7.0-STABLE | 90% |
Vulnerability description
OS Detection
Evidence
| Domain Queried | DNS Record Type | Description | Value |
|---|---|---|---|
| e-laboteka.pl | A | IPv4 address | 34.128.166.114 |
| e-laboteka.pl | NS | Name server | arely.ns.cloudflare.com |
| e-laboteka.pl | NS | Name server | ray.ns.cloudflare.com |
| e-laboteka.pl | SOA | Start of Authority | arely.ns.cloudflare.com. dns.cloudflare.com. 2415215252 10000 2400 604800 1800 |
| e-laboteka.pl | TXT | Text record | "5024c07c-ed51-4861-ae77-4bbe2d6d64ce" |
Risk description
An initial step for an attacker aiming to learn about an organization involves conducting searches on its domain names to uncover DNS records associated with the organization. This strategy aims to amass comprehensive insights into the target domain, enabling the attacker to outline the organization's external digital landscape. This gathered intelligence may subsequently serve as a foundation for launching attacks, including those based on social engineering techniques. DNS records pointing to services or servers that are no longer in use can provide an attacker with an easy entry point into the network.
Recommendation
We recommend reviewing all DNS records associated with the domain and identifying and removing unused or obsolete records.